
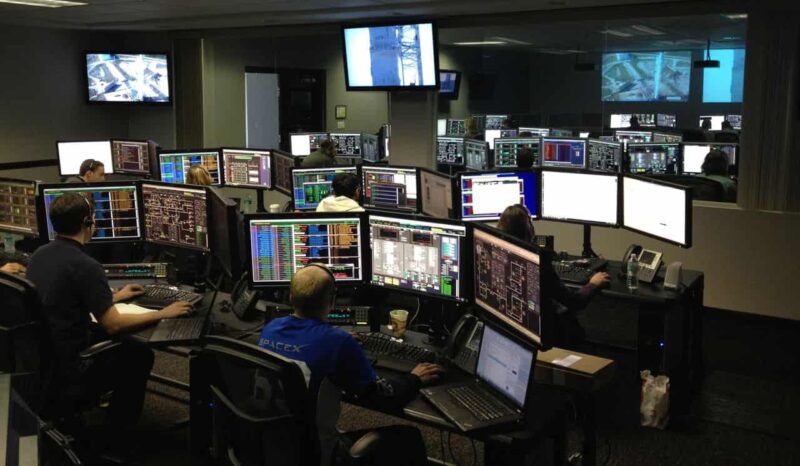
As cyber threats become more sophisticated, businesses need continuous monitoring and rapid incident response to protect their digital assets. However, building and maintaining an in-house Security Operations Center (SOC) requires significant investment in skilled personnel, advanced technology, and around-the-clock operations. For many organizations, this isn’t practical or affordable.
This is where SOC as a Service (SOCaaS) offers a cost-effective solution. SOCaaS provides businesses with outsourced security operations that include 24/7 threat monitoring, incident detection, investigation, and response. By partnering with a trusted provider, organizations gain access to experienced cybersecurity professionals and enterprise-grade security technologies without the expense of operating their own SOC.
In this guide, we’ll explain what SOC as a Service is, how it works, its benefits, and why it’s becoming an essential part of modern cybersecurity strategies.
What Is SOC as a Service?
SOC as a Service (SOCaaS) is a managed cybersecurity solution that provides organizations with continuous monitoring, threat detection, incident response, and security analysis through an external Security Operations Center.
Instead of building an internal SOC, businesses outsource these responsibilities to cybersecurity experts who use advanced monitoring tools and threat intelligence to identify and respond to potential attacks.
SOCaaS providers monitor networks, endpoints, cloud environments, servers, and applications around the clock to detect suspicious activity before it develops into a serious security incident.
How SOC as a Service Works
SOC as a Service combines experienced security analysts, automated monitoring tools, and advanced threat intelligence to protect an organization’s IT environment.
The process generally includes:
- Continuous monitoring of networks, endpoints, and cloud resources.
- Collection and analysis of security logs from multiple systems.
- Detection of suspicious behavior using advanced analytics and threat intelligence.
- Investigation of security alerts by experienced analysts.
- Rapid response to confirmed threats.
- Reporting, recommendations, and ongoing security improvements.
Many SOC providers operate 24 hours a day, 365 days a year, ensuring threats are detected even outside normal business hours.
Key Features of SOC as a Service
Modern SOCaaS solutions offer a wide range of cybersecurity capabilities.
24/7 Security Monitoring
Cyberattacks can occur at any time. SOC analysts continuously monitor your systems to identify suspicious activities before they cause significant damage.
Round-the-clock monitoring reduces response times and minimizes business disruption.
Threat Detection
SOC platforms collect data from firewalls, endpoints, cloud services, applications, and network devices.
Using Security Information and Event Management (SIEM) platforms, artificial intelligence, and behavioral analytics, security teams identify unusual activities that may indicate cyber threats.
Incident Response
When suspicious activity is confirmed, SOC analysts investigate the threat and initiate appropriate response procedures.
These may include:
- Isolating compromised devices
- Blocking malicious IP addresses
- Disabling compromised user accounts
- Containing malware infections
- Coordinating recovery efforts
Rapid response helps minimize the impact of cyber incidents.
Threat Intelligence
SOC providers continuously monitor global cyber threat intelligence feeds.
This allows analysts to recognize emerging attack techniques, newly discovered vulnerabilities, and malicious indicators before they affect client environments.
Security Reporting
Organizations receive regular reports detailing:
- Security incidents
- Threat trends
- Vulnerability findings
- Response activities
- Compliance status
- Recommendations for improvement
Detailed reporting helps leadership understand their organization’s security posture.
Also Read: Best Budgeting Apps for Students
Benefits of SOC as a Service
SOCaaS offers numerous advantages compared to maintaining an internal security operations center.
Reduced Security Costs
Building an in-house SOC requires expensive investments in technology, infrastructure, and highly skilled cybersecurity professionals.
SOC as a Service provides enterprise-level protection through a predictable subscription model, making advanced security more affordable.
Access to Cybersecurity Experts
SOC providers employ experienced security analysts, incident responders, threat hunters, and digital forensics specialists who stay current with evolving cyber threats.
Organizations gain access to expertise that may be difficult to recruit internally.
Faster Threat Detection
Continuous monitoring enables threats to be identified quickly, often before attackers achieve their objectives.
Early detection significantly reduces the risk of data breaches and operational downtime.
Improved Compliance
SOC providers help organizations meet regulatory requirements by maintaining security controls, monitoring logs, and supporting compliance with standards such as:
- HIPAA
- PCI DSS
- GDPR
- ISO 27001
- SOC 2
Strong monitoring and documentation simplify compliance audits.
Scalability
As organizations grow, their security needs become more complex.
SOCaaS solutions can easily scale to support additional users, cloud services, business locations, and connected devices without major infrastructure changes.
Industries That Benefit from SOC as a Service
SOCaaS is valuable across many industries, especially those handling sensitive information.
Common industries include:
- Healthcare
- Banking and financial services
- Retail
- Manufacturing
- Government
- Education
- Technology
- E-commerce
- Insurance
- Legal services
Businesses of every size can benefit from outsourced security operations, particularly small and medium-sized organizations with limited cybersecurity resources.
SOC as a Service vs. Traditional In-House SOC
Understanding the differences between SOCaaS and an internal SOC helps organizations choose the right approach.
In-House SOC
An internal SOC provides complete control over security operations but requires significant investment in staff, tools, infrastructure, and ongoing training. It is often best suited for large enterprises with substantial cybersecurity budgets.
SOC as a Service
SOCaaS delivers many of the same capabilities through an outsourced model. Businesses gain access to advanced technologies, expert analysts, and continuous monitoring without the high costs of building and maintaining their own security operations center.
For most small and mid-sized businesses, SOCaaS offers an excellent balance between security, expertise, and affordability.
Best Practices for Implementing SOCaaS
To maximize the value of SOC as a Service, organizations should:
- Define clear security goals and responsibilities.
- Integrate all critical systems into the SOC monitoring platform.
- Enable multi-factor authentication (MFA) for sensitive accounts.
- Keep operating systems and applications updated.
- Conduct regular employee cybersecurity awareness training.
- Review security reports and recommendations regularly.
- Test incident response and disaster recovery plans periodically.
These practices strengthen collaboration between your internal IT team and the SOC provider.
Conclusion
Cybersecurity threats continue to evolve, making continuous monitoring and rapid incident response more important than ever. SOC as a Service (SOCaaS) provides businesses with enterprise-grade security operations without the cost and complexity of building an internal Security Operations Center.
By leveraging experienced analysts, advanced threat detection technologies, and 24/7 monitoring, SOCaaS helps organizations identify threats faster, reduce security risks, improve regulatory compliance, and protect critical business assets. Whether you’re a growing startup, a mid-sized company, or a large enterprise, investing in SOC as a Service can strengthen your cybersecurity strategy and provide the resilience needed to operate confidently in today’s digital landscape.
